php2shell Security Vulnerability: Update Guidelines
Critical security vulnerabilities in PHP: The "php2shell" vulnerability allows Remote Code Execution, enabling attackers to execute malicious code on servers without authentication.
Find update guidelines and alternative protection measures in this post.

Currently, there are two critical security vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619), known as "php2shell."
Attackers can use these vulnerabilities to execute malicious code on servers from a remote location (Remote Code Execution).
A fix is available in the newly released PHP versions 8.5.12, 8.4.27, 8.3.36, and 8.2.35.
Laravel Forge temporarily unavailable
Due to high user traffic, Laravel Forge was barely accessible between 3:00 PM and 5:00 PM.
The following manual or alternative protection measures are available:
Use CloudFlare WAF, as it already provides protection against php2shell.
Take affected systems offline temporarily.
Use the PHP binary provided via https://www.php.net/downloads.php
Important note for Linux users
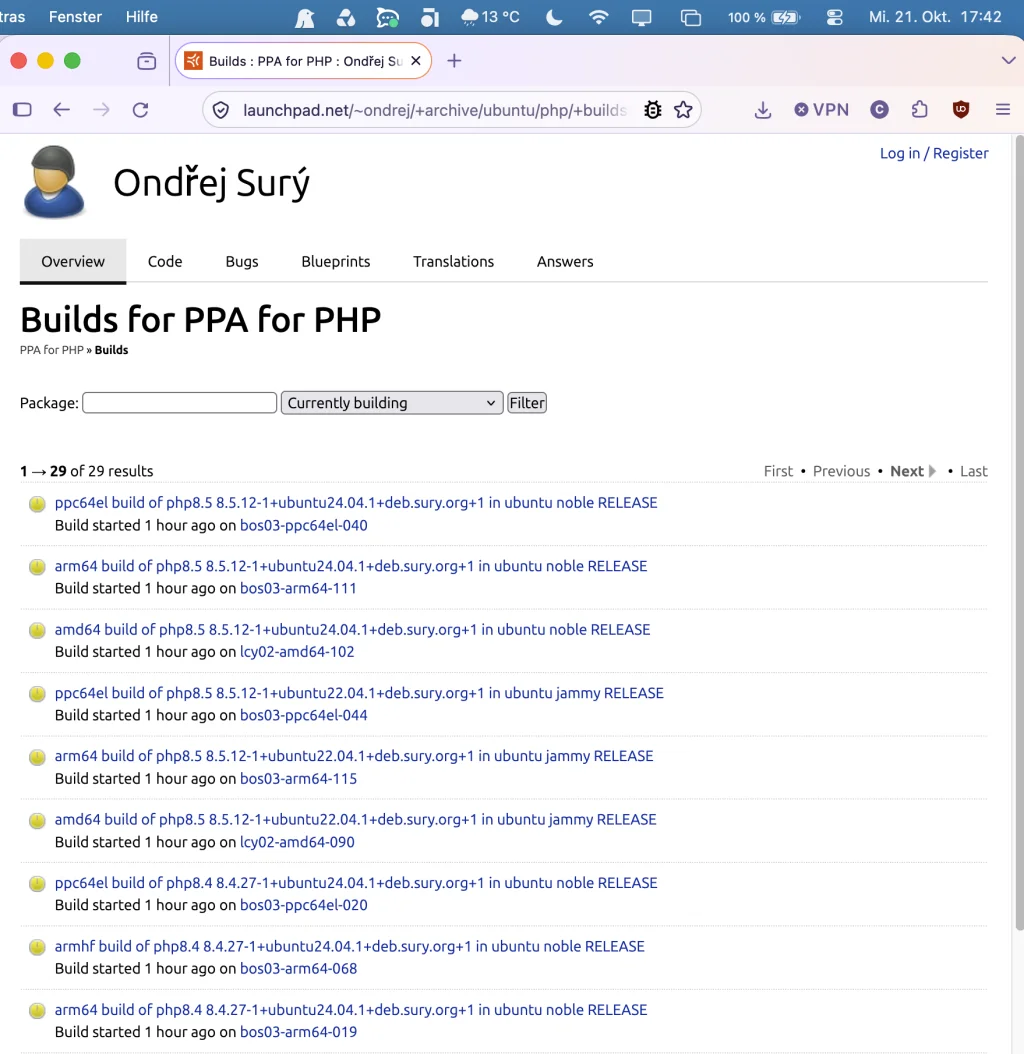
As of now (Oct 21, 2026, 5:40 PM CEST), the updated PHP packages (PPAs) are still being built.
A simple system update via "apt" does not work at the moment because the updates are not yet available.
How to check if you have already received the updated PHP version
# show current PHP version
php -v

# show current OS version
lsb_release -a

# Update
apt update

# shows status and availability in the package manager
apt policy php8.5Language:shell
Update your package-sourced to get lates PHP updates to fix php2shell
On some machines, the newly released PHP versions are not loaded immediately.
To retrieve the current package sources, follow these steps on your Ubuntu server. This tip was posted on reddit.
Remove the old package source lists
sudo rm -f /etc/apt/sources.list.d/ondrej-ubuntu-php-*.listLanguage:shellInstall the current package sources
curl -fsSL https://packages.sury.org/php/README.txt | bashLanguage:htmlYou can now get the fixed PHP version via apt update
sudo apt updateLanguage:htmlCheck the php version
php -vLanguage:htmlHow Cloudflare’s WAF protects against php2shell
The Cloudflare Web Application Firewall (WAF) acts as a shield between your website and the internet.
In the case of the php2shell vulnerability, the WAF monitors incoming requests and outgoing responses from your server and acts as a reverse proxy.
As soon as the WAF detects an attempted attack or an unauthorized data leak, it blocks the connection immediately.
This stops the attack before it can be successfully completed. This effectively protects your systems, even if the PHP update has not yet been installed, and gives you the necessary time to fix the software error.
Sources
https://www.php.net/archive/2026.php
https://blog.cloudflare.com/php-vulnerabilities-waf-protection/
https://ubuntu.com/security/notices/USN-8948-1
https://launchpad.net/~ondrej/+archive/ubuntu/php/+builds?build_state=building
https://github.com/php/php-src/security/advisories/GHSA-w8hw-w9fx-j79w
https://laravel.com/forge/docs/knowledge-base/php-security-release-october-2026
https://laravel.com/blog/php-critical-vulnerability-response-updates
https://www.reddit.com/r/PHP/comments/1xbno6r/comment/pi0mpvo
No results One result
Too many searches in a short time. The search is not reachable right now.
Please wait a moment, then carry on. Please try again in a moment.